Editor's note: This article was reviewed by the OKX Radar editorial team. In the content below, "source facts" are objective information reported by media such as Cointelegraph and Decrypt; "editorial analysis" represents OKX Radar's interpretation and operational suggestions based on public information. Data verified through 2026-09-14.
Core summary: The EU Cyber Resilience Act is now in force, requiring crypto wallet providers to submit an early report within 24 hours of discovering a vulnerability. Violations can result in administrative fines of up to €15 million or 2.5% of global annual turnover, whichever is higher. For MSX on-chain US stock users, using third-party non-custodial wallets such as MetaMask and Trezor does not create an obligation to report vulnerabilities to regulators, but users should pay attention to service providers' compliance status, data breach notices, and MetaMask anti-scam features. Data in this article verified through 2026-09-14.
1. The EU Cyber Resilience Act's 24-hour vulnerability reporting obligation: what it means for MSX on-chain US stock users' wallets
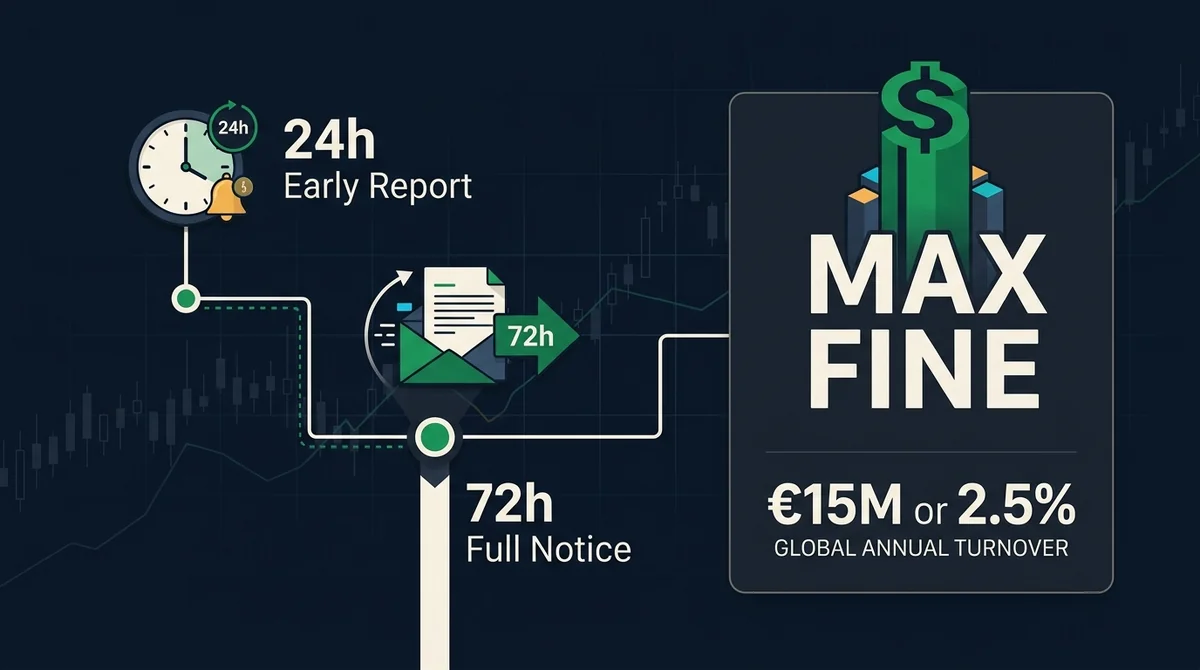
According to Cointelegraph, the EU Cyber Resilience Act is now in force, requiring crypto wallet providers to submit an early report within 24 hours and a complete notification within 72 hours of discovering a vulnerability. The obligation applies to wallet providers, not end users.
For users who hold MSX on-chain US stocks through third-party non-custodial wallets such as MetaMask and Trezor, these wallet service providers may be subject to the regulation. Based on its public positioning, MSX is an on-chain US stock trading platform and does not provide wallet services; users must choose third-party wallets themselves. End users have no obligation to report vulnerabilities to regulators.
2. Fines and compliance risks: indirect effects MSX on-chain US stock investors should watch
Non-compliant companies may face administrative fines of up to €15 million or 2.5% of global annual turnover, whichever is higher. Key deadlines and fine standards are as follows:
| Item | Requirement / Standard |
|---|---|
| Early vulnerability report | Within 24 hours of discovery |
| Complete vulnerability notification | Within 72 hours of discovery |
| Maximum administrative fine | €15 million or 2.5% of global annual turnover, whichever is higher |
If a wallet service provider is penalized or suspends service due to non-compliance, it may indirectly affect users' access to tokenized US equity assets.
As of 2026-09-14, no specific enforcement cases have been found in public sources; users should continue to monitor subsequent regulatory announcements. Choosing wallet service providers that disclose security incidents in compliance can help reduce operational risk.
3. Trezor shipping provider data breach and phishing emails: how MSX users can identify and respond
According to Cointelegraph, hardware